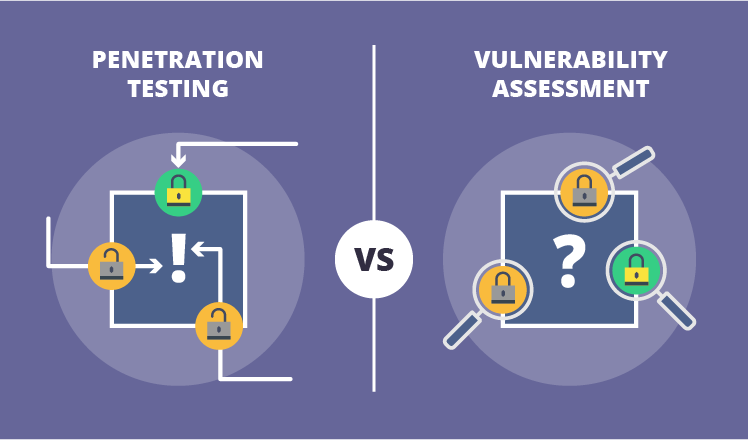
A vulnerability scan is an automated check that lists known weaknesses, while a penetration test is a manual attempt to exploit them and show real impact. Scans are cheap and frequent, and pentests are deeper and less frequent. Most businesses need both, sequenced throughout the year and aligned with compliance requirements.
Continue reading
Cyber attacks are no longer something that only happens to banks and household names. The UK government’s Cyber Security Breaches Survey 2025 found that 43% of UK businesses had experienced a breach or attack in the previous twelve months, with phishing the most common route in. For small and mid-sized organisations the cause is rarely sophisticated. It is usually an unpatched laptop, a reused password or a firewall left on its default settings.
Continue reading
First-party fraud is an awkward category for a security team, because nothing in the telemetry looks broken. The right customer logs in from a familiar device, buys something, receives it, then tells their issuer the charge was never authorized. No credential was stolen, no control failed, and the loss still lands on the merchant.
Continue reading
Most large organisations run two identity systems for the same employee. Facilities issues a badge that opens doors. On the IT side, that person also gets a login and an authenticator app. Separate teams own each one, and the two rarely change at the same moment.
Continue reading
Remote access is no longer limited to an employee logging in from home. The same path may be used by a contractor on a personal laptop or a service provider brought in for a short job. Those connections are useful, but they often extend beyond the devices and networks an organization directly manages, making it challenging to ensure security.
Securing that kind of access takes more than a tunnel into the network. Recent guidance on remote access policy treats employees and third parties as part of the same access problem rather than as separate exceptions.
Continue reading
A move is the one stretch of ordinary life when your data is no longer under your control. Your devices are in boxes, your paperwork is in a truck, your mail is being redirected, and your attention is elsewhere. Criminals know all of that, which is why moving season is quietly a good season for fraud.
The fix is to work through it in phases, because what matters three weeks out is not what matters on packing morning or during the first week in the new place. Taken in order, it is a handful of short jobs rather than a project.
Continue reading
A single merger between two security testing vendors is a business story on its own, but this particular one lines up with a broader shift the entire offensive security category has been moving toward for several years. This piece covers what that broader shift is, why the industry has been drifting away from the scheduled annual test model, and what this signals for vendors still built primarily around that older approach.
Continue reading
A company-sponsored transfer comes with somebody else arranging the details and an unspoken agreement that nobody will expect much from you for a week or two. Moving under your own steam because the job happens to be remote works differently, since there’s no package, no grace period, and no acknowledgment anywhere that your desk is currently on a highway in Nebraska.
Continue reading
Every budget cycle, security leaders face some version of the same choice. One option adds another platform to an already crowded security stack. The other invests in the people who have to operate that stack, whether through tuition assistance, professional development, or degree sponsorship.
The platform often has an easier case to make. It comes with a demo, a feature list, and a clear price. Education has a longer horizon, and its value is harder to fit into a procurement spreadsheet. However, adding another tool doesn’t necessarily solve a capability problem.
Continue reading
A “free” hotel night can become very expensive if you played longer than planned just to unlock it. That is the useful way to look at casino rewards programmes. The perks can be real, but their value depends on what you had to do to earn them.
Continue reading