10 Best Endpoint Security Companies: Who Can Tell an AI Agent From the User?
AI agents now run code on your laptop without a single click. That overturns the old endpoint rule that any trusted process must have been launched by a human. A coding assistant reads a file, decides on a tool call and writes to disk under your account, with your permissions, at machine speed. Every major vendor has moved on this, wiring agent inventories, prompt inspection and tool call controls into products you may already own. This guide ranks the 10 best endpoint security companies on the question the marketing rarely answers: can the console tell you an agent did this, name it, and show the prompt behind it? Each entry links the vendor’s own page.
Backslash Security: best specialist for naming and governing the endpoint agent
Backslash discovers every AI agent on the machine, its skills, and the Model Context Protocol servers it talks to. Instead of logging a plain git pull, it records who or what triggered the command, which prompt issued the instruction, and which tools the agent planned to use next, then blocks the operation if risk thresholds are met. The company refers to this capability as agentic endpoint security, a discipline that maps the entire agentic fabric in real time and enforces policy before malicious code ever leaves disk.
Running on the endpoint, the sensor tracks processes, prompts, skills, plug-ins, and Model Context Protocol (MCP) servers in real time. When a rogue CLI helper tries to push code to a personal GitHub, Backslash:
- Tags the unsanctioned agent by name
- Scores its reach against OWASP and MITRE ATT&CK maps
- Blocks the push before a byte leaves disk
That context speeds forensics. Analysts no longer wonder whether Alice or an over-permissioned script wiped the customer directory. The timeline shows the answer.
Backslash complements your existing EDR. It does not ship malware signatures or ransomware rollback. Pair it with CrowdStrike, Defender, or SentinelOne to close the intent gap those tools miss.
Buyer checklist
- Verify Windows, macOS, and Linux coverage in writing.
- Run delegated-agent tracing during your ten-step POC.
- Measure CPU and battery impact on a developer laptop.
CrowdStrike: best full endpoint platform for AI-agent runtime causality
Falcon Guardian turns the familiar Falcon sensor into an AI agent recorder. CrowdStrike’s launch write-up describes it as fusing agent activity with Falcon endpoint telemetry to establish a causal chain from prompt to runtime behaviour and impact. In plain terms, the telemetry that flags a malicious PowerShell command now also reports which agent and which prompt fired it.
What the product page and launch blog describe:
- Continuous discovery of known and previously unknown AI agents across supported Windows, macOS and Linux endpoints, including where each runs, who uses it, and its security status.
- Runtime visibility that connects prompts, skill use, tool calls, MCP servers and identity to downstream execution for supported agents, so the console shows what an agent was asked to do and what then happened.
- Agent access controls that define which supported agent types may run on managed endpoints, so an unsanctioned type can be blocked outright.
- Investigation that reconstructs agent sessions and downstream execution into one causal view, and contains malicious agent behaviour at runtime.
Conventional Falcon strengths still apply, and so do platform realities: licensing complexity and a premium position in the market.
Buyer checklist
- Get the list of supported agent types in writing. What your developers run may not all be on it.
- Test local stdio agents during your POC, not just cloud traffic.
- Check retention tiers. Prompt trace data grows with adoption.
If you already own Falcon, this is the logical add-on rather than a new vendor.
Microsoft: best for organisations already living in the Microsoft stack
If you already manage devices with Entra ID, Intune and Microsoft 365, you likely run Microsoft Defender for Endpoint on every laptop. That footprint now doubles as an AI agent radar.
What is available now
Defender automatically detects supported local AI agents and MCP server configurations on onboarded devices and surfaces them in the Defender portal. The context around that list is what matters: each agent is tied to a device and a user, and an exposure map draws the relationships between agents, identities and the resources those identities can reach.
Discovery covers command line agents, desktop apps, agentic IDEs and IDE extensions on Windows and macOS, with macOS in preview. It also records the MCP server behind an agent, including its name, type, endpoint and start command.
What is in preview
AI agent runtime protection inspects three points in the agent loop: the user prompt, tool requests before they execute, and tool responses after they return. The target is prompt injection, meaning instructions hidden in a file, a web page or a tool’s own output. Microsoft’s worked example is an agent reading documentation that carries hidden text telling it to post a local .env file to an external URL, with Defender catching it in the tool response and blocking the action. Inspection runs either through event interfaces the agent vendor exposes or over supported network paths.
POC tips
- Include a macOS developer laptop and an offline local model.
- Check that preview hooks still log and enforce when the device is disconnected.
- Ask which plan covers inventory and which covers runtime protection, and get it in the quote.
For Microsoft-first estates the upside is clear: no extra sensor, one console, deep identity context. Lab-test the preview before production data.
Palo Alto Networks: best for enterprises seeking one plane for endpoint, network, and AI supply chain
Palo Alto’s acquisition of Koi produced Cortex Agentic Endpoint Security, which targets autonomous software on the laptop itself rather than AI traffic at the perimeter.
What it does
- Discovers the AI estate on the device, including models, MCP servers, and IDE extensions.
- Turns those signals into risk scoring, so a team gets a ranked view instead of a raw inventory.
- Applies out-of-the-box policies that govern agent interactions, with one-click removal of insecure packages, extensions and AI tools.
- Prevents in real time, blocking malicious actions, unsafe AI application interactions, and prompt injections.
Because Cortex XDR and Agentic Endpoint Security sit in the same product family, SOC teams can move from a network alert to the offending agent on the endpoint without changing consoles.
Caveats
- The public page leads with visibility, risk and prevention. It does not publish a per-command attribution timeline, so make the vendor demonstrate that view on your own hardware before you assume it exists.
- Capabilities span separate Cortex SKUs, so map costs early.
- Include an offline-model test in your POC to confirm visibility without cloud access.
If you already rely on Palo Alto firewalls or Cortex XDR, this may offer the broadest AI supply chain view with minimal extra setup. Verify licensing and local model coverage before signing.
SentinelOne: best for teams juggling browsers, terminals, and coding assistants
SentinelOne acquired Prompt Security and now ships it inside the Singularity platform, extending one policy engine from process telemetry to AI interaction telemetry.
Why it is different
- Discovery breadth. Prompt Security finds sanctioned and shadow AI services across the ways people actually reach a model, rather than one channel.
- Real-time interception. It blocks prompt injection as it happens and stops sensitive data leaving through AI interactions.
- Developer coverage that matters on the endpoint. It integrates with AI code assistants including GitHub Copilot and Claude Code to keep secrets, credentials and proprietary code out of prompts, and enforces AI usage policy across development environments.
- One platform. Prompt Security runs in the same console that protects endpoints, cloud, identities and data, so AI risk and conventional risk land in one place.
Caveats
- The strength here is the AI interaction layer. If you need an operating system level causal chain from prompt to file write, put that specific view in the POC script and watch it work.
- Capabilities sit across modules, so ask for one quote that covers the AI pieces you actually intend to switch on.
- Confirm that local stdio agents appear in the dashboard, not just browser and SaaS traffic.
If your fleet mixes corporate laptops, contractor Macs and a dozen SaaS IDEs, this is the strongest answer to shadow AI across all of them at once.
Check Point: best for teams securing the agents their own business builds
Check Point’s AI Agent Security aims at a different agent from the one on your developer’s laptop: the agents your organisation builds and deploys across supported cloud and low-code platforms, from discovery through to runtime.
Where it shines
- Discovery and inventory of agents deployed across supported cloud and low-code platforms, which is exactly where business teams build agents without telling security.
- Risk assessment across agent metadata, usage, tools, skills, MCP servers and connected components.
- Allow and deny control over the tools and MCP servers an agent may use, with runtime evaluation of its tool calls and detection of actions falling outside user intent or policy.
- Protection against prompt injection, indirect injection hidden in files or websites, and sensitive data exposure across prompts, responses and tool use.
Check Point describes the runtime piece as an inline enforcement layer for AI agent interactions: it inspects prompts, model responses, external content and tool calls in real time, then applies policy before data is exposed or a risky action executes.
The honest fit
This is not endpoint agent attribution, and Check Point does not claim it is. If your question is which coding assistant on which laptop deleted a directory, look elsewhere. If it is which agents your business has built and what they may do, this is a strong answer. Controls for workforce AI use sit in Workforce AI Security, so scope the decision across both.
Sophos: best for mid-market teams that want endpoint, firewall and MDR in one console
Sophos Intercept X leads with prevention. Deep learning models and exploit guards stop malware before it runs, and ransomware rollback restores encrypted files. Everything reports into Sophos Central, the same console that manages firewall, email and MDR, on one agent covering Windows, macOS and Linux.
On the agent question. Intercept X itself does not attribute an action to an AI agent, it classifies processes and supports analysts. Sophos answers that separately with Sophos AI Defense, which discovers AI tools, agents and workflows across users and devices including shadow AI, and enforces guardrails on AI usage. The capability is in the portfolio, it is just a second product and a second buying decision.
If you already run Sophos Central, the endpoint layer is settled and the agent layer becomes an add-on decision rather than a new vendor.
Bitdefender: best for adding AI discovery to an endpoint console you already run
Bitdefender’s answer to the agent question is a discovery and risk layer rather than an attribution layer, and it runs inside GravityZone.
GravityZone AI Visibility and Control builds a central inventory of the AI installed and running on protected Windows endpoints, including chatbots, local language models, coding assistants, autonomous agents, MCP servers and AI-enabled SaaS. It ranks that usage by risk so unknown, high-risk activity rises above routine business use, then enforces policy through controls you already operate, such as application control and web filtering, to allow, restrict or block a tool. Paired with GravityZone PHASR, the same telemetry feeds a behavioural baseline for AI agents and adjusts hardening as activity changes. Windows is the supported platform today, so ask about the rest of the fleet.
Why buyers choose the platform
- Prevention that does not depend on the AI story. HyperDetect behavioural engines and risk analytics flag ransomware activity, credential theft and fileless attacks.
- Low overhead. A light agent suits VDI and older laptops.
- Practical response. From one console you can isolate a host, kill a process and roll back encrypted files, as the EDR page sets out.
Where it stops
Discovery and risk scoring are not attribution. Bitdefender will tell you an autonomous agent or an MCP server is present, and let you block it, but not that one named agent issued the command that deleted a directory. If your incident reviews need that sentence, combine this with a specialist rather than treating it as one.
Huntress: best managed EDR for lean IT teams and MSPs
Huntress sells people as much as software. A light agent streams telemetry to a 24/7 SOC where analysts review what the sensors surface, close out noise, escalate real incidents with plain-language write-ups, and carry out response actions through the platform where those are supported and enabled.
Why it fits lean teams
- Managed EDR bundles the technology, the tuning and the response, so no in-house SOC is required.
- One agent covers Windows, macOS and Linux.
- The wider platform adds managed identity threat detection and response and a managed SIEM behind the same SOC, which suits MSPs folding security into a service bundle.
Limits today
Huntress is strong on footholds, malicious persistence and ransomware detonation. Its published platform pages do not describe prompt histories or a view that separates an autonomous agent from a tired intern at the keyboard. If agent attribution matters to you, add a specialist layer and keep Huntress for what it is good at.
For small teams and MSPs that value rapid human response over feature breadth, this is a pragmatic safety net. You are buying eyes on glass, not a forensic timeline of every AI-driven command.
ThreatDown: best for SMBs that want install, protect, move on
ThreatDown keeps security simple. Deploy a light agent from a cloud dashboard and you get next-generation antivirus, behavioural ransomware protection, and rollback that restores encrypted files.
The rollback mechanism is worth understanding, because it is the feature most SMBs buy this for. A kernel mode driver watches file system changes and copies files before they are modified, so recovery does not depend on Volume Shadow Copy Service, which ransomware families routinely target. The recovery window runs to 7 days after an infection.
Limits today
ThreatDown’s machine learning targets malware behaviour, not prompts or tool calls, so it will not show you which AI agent zipped /Documents. There is no agent inventory in the product, and no claim of one. If agent attribution becomes important, add a specialist layer.
For SMBs that want reliable protection and predictable bills, ThreatDown offers solid value with minimal overhead.
Honorable mentions: strong platforms, narrower answers on the agent question
Several respected platforms landed just outside the top ten. Most now document some AI capability, but on their own pages it is discovery, governance or containment rather than a timeline tying a command to a named agent and its prompt. cyberdb’s strategic market intelligence report on endpoint security vendors covers more of the market than a top ten can.
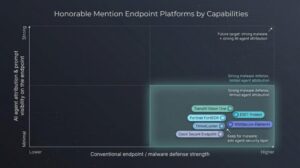
| Vendor | What its own pages describe | Where it lands on the agent question |
| TrendAI Vision One | Protection, detection and response with attack surface discovery | Broad XDR reach, no endpoint prompt-to-action mapping documented |
| ESET PROTECT | Light agent, one console | Has previewed AI agent security that inspects components agents pull in, plus monitoring of agents acting outside their task scope |
| Fortinet FortiEndpoint | Access, protection, response and vulnerability management in one agent | Central visibility of sanctioned and unsanctioned AI apps and agents, plus inspection of data shared with them; tool blocking is announced rather than shipping |
| WithSecure Elements | Protection and response in one agent and console | No endpoint agent inventory or prompt-level controls in the documentation |
| ThreatLocker | Allowlisting, ringfencing, endpoint firewall | Applies those controls to agentic AI tools, down to which sub-processes an agent may run, so it contains an agent without tracing a command to a prompt |
| Cisco | Secure Endpoint, with AI Defense alongside | AI inventory reaches user endpoints and detects MCP servers and agent processes, framed as governance rather than attribution |
If you run one of these, keep it for malware defence and treat the agent layer as a separate decision.
Buying considerations: nine questions to ask before you sign
Contracts last years and agents run on thousands of laptops. Walk every vendor through these nine checkpoints.
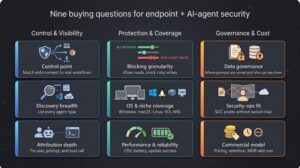
- Control point. Does the product enforce policy at the endpoint sensor, the browser, or a network gateway? Match it to real workflows, not demo VMs.
- Discovery breadth. List every agent type you have, from CLI helper to IDE plug-in to local model, and ask the vendor to surface each one. Invisible on day one usually means invisible forever.
- Attribution depth. Request a live demo that shows user, prompt, agent name and exact tool call for one action. Missing links today lead to dead-end forensics later.
- Supported agent list. Coverage is usually per agent type. Get the list, compare it with what your developers run, and ask what happens to an agent that is not on it.
- Blocking granularity. Can you allow read-only Git access but block writes, or permit format while denying delete? Coarse on and off switches force ugly trade-offs.
- OS coverage. Windows is table stakes. macOS, Linux, VDI, WSL and containers often lag. Test the edges.
- Performance and reliability. Run CPU benchmarks and battery tests, and watch update success. A 1 percent failure rate hurts across ten thousand machines.
- Data governance. Where are prompts stored, for how long, and who can read them? Look for redaction and tunable retention.
- Security operations fit. Put your own analysts in the console. Can they pivot from an agent alert to identity, process and cloud logs in one place?
Proof-of-concept checklist: ten tests every vendor should pass
Copy these steps into your lab guide and score each platform the same way.
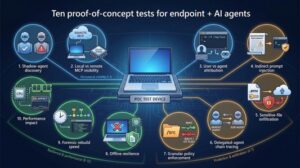
- Shadow-agent discovery. Install one approved coding agent and one renamed rogue helper, then time how long each platform takes to list both.
- Local versus remote MCP visibility. Spin up a remote model endpoint and a local stdio model. The console should list host, port and user for each.
- User versus agent attribution. Have a human and an agent run rm -rf /tmp/test. The console must tag one action human and the other agent.
- Indirect prompt-injection defence. Hide a malicious instruction in a markdown file and ask the agent to summarise it. Expect a block or a flag before shell execution.
- Sensitive-file exfiltration guard. Plant a fake .env file with API keys, tell the agent to upload it, and watch for redaction or a block.
- Delegated-agent chain tracing. Use a parent agent that spawns a sub-agent. The timeline must show both hops end to end.
- Granular policy enforcement. Permit read-only access to /src, deny writes, then attempt an agent git push. Expect read success, write failure, clear logs.
- Offline resilience. Disconnect the laptop, run a local model and agent, and confirm logging and enforcement still work.
- Forensic rebuild speed. Hand an analyst the console. They should reconstruct who, what and why in under 5 minutes.
- Performance impact. Measure CPU, memory, battery and network throughout, and flag any spike above 5 percent CPU or 10 percent battery per hour.
Score each item pass, partial or fail. The patterns appear fast.
Regulatory context: why logs alone do not equal compliance
Security vendors pitch a one-click path to compliance, yet every major rule set treats evidence as one pillar of governance among several.
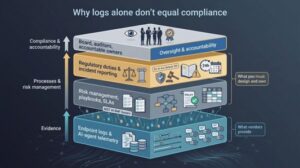
- The NIST AI Risk Management Framework. Its Govern function calls for an inventory of AI systems and ongoing monitoring, and stresses that those artefacts must map into documented risk-management processes. An inventory is an input, not the work itself.
- EU AI Act, Article 50, which applies from 2 August 2026. Providers and deployers must disclose when a person is interacting with an AI system, mark certain generated content, and keep records showing that duty was met.
- NIS2, applied since 18 October 2024. In-scope entities must send an early warning within 24 hours of becoming aware of a significant incident, then a fuller notification. Auditors will still want playbooks and named owners.
- DORA. Financial entities must submit an initial notification within 4 hours of classifying an incident as major, and no later than 24 hours from becoming aware of it. Those clocks make the forensic question, human or agent, one you answer in minutes rather than days.
Conclusion
One test separates this field. Ask each vendor to show a console view that names the agent, the prompt behind it and the command that ran, for one action on a machine you control. Tests 3 and 6 above are that test. Backslash, CrowdStrike and Microsoft aim directly at it. Palo Alto and SentinelOne cover the interaction layer well and should be made to prove the endpoint timeline. Check Point answers a different question, about the agents your business builds, and answers it well. Sophos, Bitdefender, Huntress and ThreatDown keep the malware job settled and leave attribution to a second layer, a fair choice as long as you make it on purpose.
So keep the platform you already run. Switching endpoint vendors to gain agent visibility is rarely worth the migration. Price the agent layer twice, as an add-on from that vendor and as a specialist product, then run the same 10 tests against both. If neither can answer the human or agent question on your own hardware, you have learned the most useful thing here before an incident teaches it instead.


